Day: July 30, 2026

Another Material Element Of Roaring Slot Strategies Is Roll DirectionAnother Material Element Of Roaring Slot Strategies Is Roll Direction

Online slots are a nonclassical form of entertainment that continues to develop with advancements in applied science. While many players go about slot games purely for fun, there is a growth interest in sympathy and utilizing strategies to raise the gaming experience. In this article, we dig in into the earthly concern of online slot strategies, discovery the potency benefits they can offer to players.

The Psychology Behind Slot Strategies

Contrary to popular impression, online slot games are not strictly based on luck. Behind the flash lights and spinning reels lies a algorithmic program that determines the final result of each spin. By sympathy the psychological science behind slot strategies, players can make enlightened decisions that may step-up their chances of winning.

Utilizing Probability Analysis

One key view of effective slot strategies is probability psychoanalysis. By studying the odds of certain outcomes and adjusting their gameplay accordingly, players can optimise their successful potency. This deductive go about sets strategic players apart from those who rely solely on chance.

Implementing Bankroll Management

Another crucial element of roaring slot strategies is bankroll direction. By scene limits on how much to bet and knowing when to walk away, players can keep up their gaming sessions and downplay losses. Smart budgeting is a of property and pleasant slot gameplay.

Recent Industry Insights

According to Recent epoch statistics from the Online Gambling Market Report 2021, the online slot industry is experiencing significant increment, with a projected CAGR of 8.6 from 2021 to 2026. This upwards slew indicates a rise demand for online slot games and presents opportunities for players to search groundbreaking strategies.

The Shift Towards Skill-Based Gameplay

One luminary swerve in the online slot manufacture is the transfer towards science-based gameplay. As players seek more engaging and appreciated gaming experiences, developers are incorporating that want strategy and decision-making. This evolution opens up new possibilities for players to apply high-tech strategies and enhance their gameplay.

The Rise of Data-Driven Strategies

In a data-driven earthly concern, online slot players are leveraging analytics and insights to rectify their strategies. By trailing public presentation prosody, analyzing trends, and adapting their approach supported on data, players can gain a aggressive edge in the moral force online slot landscape. The product of data skill and play is reshaping the way players go about slot strategies.

Maximizing Wins with Strategic Play

Ultimately, the goal of employing บาคาร่าเว็บตรง slot strategies is to maximize wins and lift up the gambling experience. Whether through measured risk-taking, disciplined gameplay, or innovational approaches, strategic players have the potency to unlock new levels of use and rewards in the worldly concern of online slots.

Conclusion

As online slot games bear on to germinate, so do the strategies that players can use to enhance their gameplay. By embrace the psychology behind slot strategies, leverage Holocene manufacture insights, and adopting a data-driven set about, players can unlock a worldly concern of possibilities within the online slot landscape painting. Whether you re a veteran participant or new to the game, exploring hi-tech strategies can add depth and exhilaration to your

Wak89 Situs Slot dan Casino Online yang Sedang ViralWak89 Situs Slot dan Casino Online yang Sedang Viral

Dalam beberapa waktu terakhir, dunia hiburan digital kembali diramaikan dengan munculnya berbagai platform permainan online yang semakin canggih dan menarik. Salah satu nama yang cukup sering dibicarakan adalah Wak89. Situs ini dikenal sebagai platform slot dan casino online yang sedang viral dan banyak menarik perhatian pemain dari berbagai kalangan.

Namun, apa sebenarnya yang membuat Wak89 begitu cepat populer? Apakah hanya sekadar tren, atau memang ada sesuatu yang membuatnya berbeda dari platform lainnya? Mari kita bahas lebih dalam dengan gaya yang santai namun tetap informatif.

Mengapa Wak89 Bisa Menjadi Viral?

Tidak semua situs permainan online bisa langsung viral. Biasanya, ada kombinasi faktor yang membuat sebuah platform cepat dikenal dan dibicarakan.

Pengalaman Bermain yang Lebih Modern

Salah satu alasan utama Wak89 menjadi viral adalah karena pengalaman bermainnya yang terasa lebih modern. Tampilan antarmuka yang sederhana namun elegan membuat pemain baru tidak merasa kesulitan saat pertama kali mengakses platform ini.

Selain itu, respons sistem yang cepat juga memberikan kenyamanan tersendiri, terutama bagi pemain yang menginginkan permainan tanpa gangguan teknis.

Variasi Permainan yang Menarik

Wak89 menawarkan berbagai jenis permainan slot dan casino yang bisa dipilih sesuai selera pemain. Mulai dari slot dengan tema klasik hingga permainan dengan visual modern yang lebih interaktif.

Keberagaman ini membuat pemain tidak cepat bosan karena selalu ada pilihan baru yang bisa dicoba.

Fitur Unggulan yang Membuat Wak89 Dilirik

Di tengah banyaknya platform sejenis, Wak89 mencoba menonjol dengan beberapa fitur unggulan yang menjadi daya tarik utama.

Sistem yang Lebih Stabil

Stabilitas sistem menjadi salah satu faktor penting dalam dunia permainan online. Wak89 dikenal memiliki performa server yang cukup stabil, sehingga pemain bisa menikmati permainan tanpa gangguan yang berarti.

Hal ini memberikan pengalaman bermain yang lebih lancar dan menyenangkan.

Akses yang Lebih Fleksibel

Salah satu keunggulan lain adalah fleksibilitas akses. Pemain dapat menikmati permainan melalui berbagai perangkat, termasuk smartphone dan komputer, tanpa kehilangan kualitas tampilan.

Ini membuat Wak89 cocok untuk gaya hidup modern yang serba cepat dan mobile.

Antarmuka yang Ramah Pengguna

Desain yang sederhana namun tetap menarik membuat Wak89 mudah digunakan oleh siapa saja, termasuk pemain pemula. Navigasi yang jelas membantu pemain menemukan permainan yang mereka inginkan dengan cepat.

Daya Tarik Bonus dan Promo

Dalam dunia slot dan casino online, bonus selalu menjadi daya tarik utama. Wak89 juga menawarkan berbagai bentuk bonus yang membuat pemain semakin tertarik untuk mencoba.

Bonus Awal untuk Pemain Baru

Pemain baru biasanya mendapatkan bonus awal sebagai bentuk sambutan. Bonus ini memberikan kesempatan untuk mencoba berbagai permainan tanpa harus langsung menggunakan modal besar.

Promo Berkala yang Menarik

Selain bonus awal, terdapat juga promo berkala yang diberikan pada waktu tertentu. Promo ini sering menjadi momen yang ditunggu oleh para pemain aktif.

Bonus sebagai Pendukung, Bukan Tujuan Utama

Meski bonus terlihat menggiurkan, pemain bijak biasanya tidak hanya fokus pada bonus semata. Mereka memahami bahwa bonus hanyalah tambahan, bukan jaminan kemenangan.

Pengalaman Bermain yang Lebih Seru

Wak89 tidak hanya menawarkan permainan, tetapi juga pengalaman hiburan yang lebih lengkap.

Sensasi Slot yang Lebih Hidup

Permainan slot di Wak89 dirancang dengan visual yang menarik dan efek suara yang membuat pengalaman bermain terasa lebih hidup. Hal ini memberikan sensasi hiburan yang lebih imersif bagi pemain.

Interaksi dalam Permainan Casino

Untuk permainan casino, wak89 menghadirkan pengalaman yang lebih realistis sehingga pemain bisa merasakan atmosfer seperti berada di casino sungguhan.

Pentingnya Bermain dengan Bijak

Meskipun Wak89 menawarkan banyak hiburan, penting untuk selalu menjaga keseimbangan dalam bermain.

Tetapkan Batasan Diri

Pemain disarankan untuk menentukan batas waktu dan pengeluaran sebelum mulai bermain. Hal ini membantu menjaga pengalaman tetap menyenangkan dan tidak berlebihan.

Jadikan Hiburan, Bukan Beban

Permainan online sebaiknya dipandang sebagai hiburan, bukan sebagai sumber tekanan atau harapan utama. Dengan mindset yang tepat, pengalaman bermain akan terasa lebih santai.

Kesimpulan

Wak89 berhasil menjadi salah satu situs slot dan casino online yang sedang viral berkat kombinasi antara tampilan modern, variasi permainan yang lengkap, serta pengalaman bermain yang nyaman.

Namun, di balik semua itu, kunci utama tetap ada pada cara pemain menikmati permainan. Dengan sikap yang bijak dan terkontrol, Wak89 bisa menjadi sarana hiburan digital yang menyenangkan tanpa harus berlebihan.

Pada akhirnya, bukan hanya platform yang menentukan pengalaman, tetapi juga bagaimana pemain mengelola diri mereka saat bermain.

Are dynamic QR codes secure?Are dynamic QR codes secure?

Dynamic QR codes are generally secure when they are created, managed, and used properly, but they are not automatically safe simply because they are called “dynamic.” Like any other digital technology, their security depends on how the system behind them is designed and how people use them.
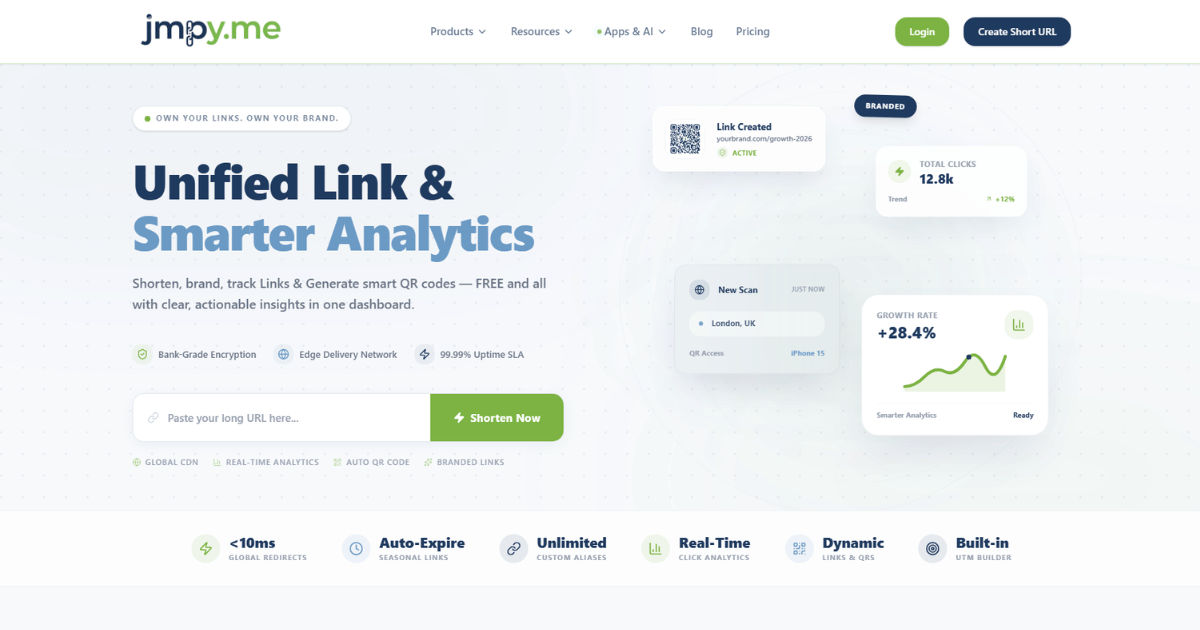
If you are looking for Dynamic qr codes free tools, you may find many services that allow you to create editable QR codes without paying. However, before choosing a free platform, it is important to understand what happens when someone scans your QR code. A dynamic QR code usually does not contain the final destination directly. Instead, it often sends the scanner to a short or controlled URL that redirects them to the actual website, landing page, menu, payment page, form, or other content.

This ability to change the destination later is one of the main advantages of dynamic QR codes. It is also one of the reasons security deserves attention.

A static QR code usually contains fixed information. Once it has been printed, the information inside it generally cannot be changed without creating a new QR code. A dynamic QR code works differently. The destination can often be updated through an online dashboard without changing the printed code.

That flexibility is useful for businesses, schools, events, restaurants, marketing campaigns, and many other situations. But it also means that control over the QR code account, redirect system, and destination URL becomes extremely important.

So, are dynamic QR codes secure?

The short answer is: they can be secure, but security depends on the platform, configuration, account protection, destination website, and the behavior of the person scanning the code.

Understanding these factors can help you use dynamic QR codes safely without unnecessary fear or confusion.

How Dynamic QR Codes Work

To understand their security, it helps to first understand how dynamic QR codes actually work.

When you scan a typical dynamic QR code, the QR code itself may not contain the final website address. Instead, it contains a URL connected to a QR code management service.

The scanning process may look something like this:

You open your phone's camera.

You point it at the QR code.

Your phone reads the encoded URL.

The URL opens in your browser.

The QR service processes the request.

You are redirected to the final destination.

The final destination could be a website, online menu, registration form, social media page, payment page, app download page, or another digital resource.

This system makes the QR code editable.

For example, imagine a restaurant prints thousands of QR codes on table cards. The restaurant initially uses the QR code to open a lunch menu. Later, the restaurant changes its menu.

With a dynamic QR code, the business can update the destination through its QR management platform. Customers can continue scanning the same printed QR code, while the destination changes behind the scenes.

This is convenient, but it creates an important security consideration.

Someone who controls the dynamic QR code account may be able to change where the QR code sends users.

That means account security is extremely important.

Why Dynamic QR Codes Can Be Secure

Dynamic QR codes are not inherently dangerous.

In fact, they can be secure when implemented using reputable services and good security practices.

The QR code itself is simply a way of encoding information. The bigger security questions usually involve the infrastructure surrounding it.

A secure dynamic QR code system may include encrypted connections, secure account authentication, access controls, reliable redirect systems, monitoring, and protection against unauthorized changes.

For example, a business might use a professional QR management platform that protects its administrative dashboard with strong passwords and multi-factor authentication.

If the business also uses HTTPS for its destination website, keeps its software updated, and limits account access to trusted employees, the overall setup can be reasonably secure.

The important point is that QR code security is not just about the black-and-white square pattern.

It involves the entire journey from scanning to reaching the final destination.

The Biggest Security Risk: The Destination Can Change

One of the main differences between static and dynamic QR codes is that dynamic QR codes can often be modified after they are created.

This is useful, but it introduces a potential risk.

Imagine that a company prints a dynamic QR code on a brochure. The brochure is distributed to thousands of customers.

Later, an attacker gains unauthorized access to the company's QR code management account.

If the attacker can modify the QR code destination, they may redirect users to a fake website.

The printed QR code itself has not changed.

The physical code still looks exactly the same.

However, the destination behind it has changed.

This is why businesses should protect the accounts used to manage dynamic QR codes.

A strong password, multi-factor authentication, limited administrative access, and regular account monitoring can significantly reduce this risk.

Can Dynamic QR Codes Be Hacked?

Yes, but the situation is often misunderstood.

A QR code is not usually “hacked” in the same way that a computer or server might be hacked. In many cases, the real target is the system or account that controls the QR code.

An attacker might attempt to:

Steal login credentials.

Take control of a QR management account.

Compromise the redirect service.

Modify a destination URL.

Replace a QR code with a malicious one.

Create a fake QR code that looks legitimate.

Exploit weaknesses in the destination website.

The risk depends heavily on the environment in which the QR code is being used.

For example, a company that protects its QR management account properly may have a much lower risk than a business that uses a shared password across multiple employees.

Security should therefore be considered at every stage.

QR Code Phishing Is a Real Threat

One of the most important security concerns involving QR codes is phishing.

QR phishing is sometimes called “quishing.”

The idea is simple.

An attacker creates or distributes a QR code that sends people to a fake website.

The fake website may look like a legitimate banking service, payment provider, email login page, delivery company, or social media platform.

The victim scans the QR code and follows the link.

Because the QR code is designed for scanning rather than reading, the user may not immediately notice where the link leads.

This can make QR codes useful to attackers who want to hide suspicious URLs.

For example, a person might receive a fake notice containing a QR code and a message saying that they need to confirm a payment.

The victim scans the code.

The QR code opens a fraudulent website.

The fake website asks for a username, password, card information, or other sensitive details.

The victim believes they are completing a normal process, but their information is actually being collected by the attacker.

This is not necessarily a weakness in dynamic QR codes themselves.

It is a form of social engineering that uses QR codes as the delivery method.

Why People Trust QR Codes Too Easily

QR codes have become part of everyday life.

People see them in restaurants, stores, advertisements, parking areas, product packaging, posters, and business cards.

Because QR codes are now familiar, people often scan them without thinking carefully about where they will lead.

This creates an opportunity for attackers.

A QR code does not visually tell you whether it is trustworthy.

A malicious QR code can look almost identical to a legitimate one.

That is why users should develop the habit of checking the destination before entering sensitive information.

If you scan a QR code and your browser opens a website asking for your banking password, payment information, or account credentials, take a moment to verify the website address.

Do not assume the page is legitimate simply because the QR code was printed on a professional-looking poster.

Can Dynamic QR Codes Track Users?

Potentially, yes.

One advantage of dynamic QR code systems is that they can provide analytics.

Depending on the service, the QR code owner may be able to see information such as:

How many times the code was scanned.

When scans occurred.

The general location associated with scans.

The type of device used.

The operating system.

The browser or technical information.

This data can be valuable for marketing and operational purposes.

A business might use it to determine which advertising campaign receives the most engagement.

However, tracking also raises privacy questions.

The exact information collected depends on the QR code platform, its privacy policies, and the analytics configuration.

If privacy is important, businesses should understand what information is collected and how long it is retained.

Users should also be cautious about scanning QR codes that lead to websites requesting unnecessary personal information.

Security and privacy are related, but they are not exactly the same thing.

A QR code can be technically secure while still being used in a way that collects more user data than necessary.

Are Free Dynamic QR Code Services Safe?

Searching for Dynamic qr codes free services can be a good way to experiment with the technology, but free does not automatically mean secure or insecure.

The important question is not simply whether the service costs money.

Instead, you should examine how the service handles security.

Before using a free dynamic QR code platform, consider whether it provides HTTPS connections, account protection, reliable customer support, clear privacy policies, and transparent information about how QR codes are managed.

You should also understand whether the QR code remains active permanently or whether it expires after a certain period.

Some free services may have limitations.

For example, a service might restrict the number of scans, provide fewer analytics features, display branding, or require an upgrade later.

The biggest concern is whether you fully understand what happens to your QR code and its destination.

If a QR code is being used for something important, such as a business campaign, public information, or customer access, it may be worth choosing a provider with a strong reputation and clear security practices.

Free tools can be useful, but convenience should not come at the expense of security.

The Importance of HTTPS

HTTPS is one of the basic security features you should look for when using QR codes.

When a QR code directs users to a website, the website should ideally use HTTPS.

HTTPS encrypts the connection between the user's browser and the website.

This helps protect information transmitted during the connection.

You can usually identify HTTPS by looking for a URL that begins with “https” and a browser security indicator.

However, HTTPS does not automatically mean that a website is trustworthy.

This is an important distinction.

A malicious website can also use HTTPS.

The encryption protects the connection, but it does not guarantee that the website owner is legitimate.

Therefore, users should consider both the security of the connection and the identity of the website.

A fake website can have HTTPS and still be designed to steal passwords.

Dynamic QR Codes and Payment Security

Payment-related QR codes require extra caution.

QR codes are increasingly used for digital payments, bills, donations, and other financial transactions.

If you scan a payment QR code, always verify the payment details before confirming the transaction.

Check the recipient.

Check the amount.

Check the payment app.

Check the transaction information.

An attacker could potentially replace a legitimate payment QR code with another code that sends money to a different recipient.

This is especially important in public places.

For example, a QR code displayed at a store, parking area, or donation location could potentially be replaced or covered by a malicious QR code.

Businesses should physically inspect important QR codes and consider tamper-resistant displays.

Customers should also verify the recipient before completing a payment.

A QR code can make the payment process faster, but it should not remove the normal verification step.

Physical QR Code Tampering

Not every QR code attack happens online.

Physical tampering is another concern.

An attacker may place a sticker containing a malicious QR code over a legitimate QR code.

This can happen in public spaces where QR codes are displayed openly.

For example, a criminal could place a fake QR sticker over a restaurant menu QR code.

Customers scan the replacement code and are sent somewhere else.

The fake code may lead to a phishing website or another malicious destination.

Businesses can reduce this risk by regularly inspecting printed QR codes.

They can also use high-quality printing, tamper-resistant materials, and designs that make unauthorized replacement more obvious.

Customers should be cautious when a QR code appears to have been placed over another code or looks damaged, poorly printed, or suspicious.

How Businesses Can Make Dynamic QR Codes Safer

Businesses that use dynamic QR codes should treat them as part of their digital infrastructure.

The first step is to protect the account that controls the QR codes.

Use a strong, unique password.

Enable multi-factor authentication whenever possible.

Do not share administrator credentials.

Remove access for employees who leave the organization.

Limit administrative privileges to people who actually need them.

These basic practices can prevent many common account-related problems.

Businesses should also keep an inventory of their active QR codes.

Know where each code is displayed.

Know which destination it should open.

Know who manages it.

Know when it was last reviewed.

This makes it easier to detect unexpected changes.

Regularly test important QR codes as well.

A code that worked six months ago may not work today if a service has changed its policies or the destination website has been removed.

How Users Can Safely Scan Dynamic QR Codes

Users can also take simple steps to protect themselves.

First, think about where the QR code came from.

Was it provided by a trusted business?

Was it sent unexpectedly?

Was it attached to a suspicious message?

Was it displayed in a public location?

Context matters.

After scanning, look at the destination URL before continuing.

If the address looks strange, contains unexpected spelling, or appears unrelated to the organization you expected, stop.

Do not enter passwords or financial information until you are confident that the website is legitimate.

You should also avoid downloading unknown applications simply because a QR code tells you to do so.

If an app is required, consider finding it through your device's official app store and searching for the legitimate application yourself.

The safest approach is not to panic about QR codes.

Instead, treat them like links.

You would not click an unfamiliar link in an email without thinking.

The same principle should apply to QR codes.

Dynamic QR Codes vs Static QR Codes: Which Is Safer?

Neither type is automatically safer in every situation.

Static QR codes have a fixed destination.

Once created, the information encoded into them generally cannot be changed.

This can reduce the risk of unauthorized destination changes.

However, a static QR code can still be malicious from the beginning.

If someone creates a static QR code pointing to a phishing website, it remains dangerous even though it cannot be dynamically edited.

Dynamic QR codes provide flexibility.

The destination can be updated without replacing the physical code.

This is highly useful, but it creates an additional security responsibility.

The account or system controlling the QR code must be protected.

In simple terms, static QR codes generally have fewer moving parts, while dynamic QR codes offer more flexibility but require stronger management.

The safer choice depends on the specific use case.

What Makes a Dynamic QR Code Platform Trustworthy?

When selecting a dynamic QR code provider, do not focus only on price.

Look at the overall service.

A trustworthy platform should have clear information about how its system works.

It should explain how QR codes are managed and what security measures are available.

Look for features such as secure login systems, multi-factor authentication, HTTPS, account access controls, reliable uptime, and clear privacy policies.

It is also useful to check how the company handles support and account recovery.

Imagine that your business has printed thousands of QR codes and suddenly loses access to the management account.

How easily can you recover it?

What happens if an employee who manages the account leaves?

Can you transfer ownership?

Can you control multiple users?

These practical questions can be more important than simply finding the cheapest option.

Common Mistakes That Reduce QR Code Security

One common mistake is using the same password for the QR management account and other services.

If that password is stolen elsewhere, attackers may attempt to use it to access the QR platform.

Another mistake is giving every employee administrator access.

Most employees do not need full control over QR codes.

Access should be limited according to responsibility.

Another problem is failing to review old QR codes.

A business may create hundreds of codes over several years and forget about some of them.

Old codes should be reviewed and disabled when they are no longer needed.

Businesses should also avoid placing sensitive information directly into QR codes when it is unnecessary.

The QR code should direct users to a secure system rather than exposing confidential information in a way that can easily be copied.

What Should You Do If a QR Code Looks Suspicious?

If a QR code looks suspicious, do not scan it.

If you already scanned it, do not automatically assume that something bad has happened.

Check what website opened.

If the page looks unusual, close it.

Do not enter your password or payment details.

If you entered sensitive information on a suspicious website, take immediate steps to protect the affected account.

Change the password from a trusted device.

Enable multi-factor authentication if available.

Monitor your accounts for unusual activity.

If financial information was submitted, contact the relevant financial institution through its official contact channels.

The most important thing is to respond quickly rather than panic.

Are Dynamic QR Codes Secure for Businesses?

Yes, dynamic QR codes can be secure enough for many business applications when managed correctly.

They are commonly useful for menus, marketing campaigns, event registration, product information, customer feedback, and other applications.

However, businesses should recognize that a QR code is part of a larger system.

Security should include the QR management account, redirect service, destination website, analytics system, employees who have access, and physical locations where the codes are displayed.

A business that protects only the website but ignores the QR management account may still have a security weakness.

Good security is about protecting the entire process.

Are Dynamic QR Codes Safe for Personal Use?

For ordinary personal use, dynamic QR codes can be perfectly reasonable.

You might use one to share a personal website, portfolio, event invitation, or contact information.

The same basic rules apply.

Use a reputable platform.

Protect your account.

Check the destination.

Avoid entering sensitive information on unexpected websites.

If you are scanning someone else's QR code, verify the destination before taking action.

Personal use usually involves fewer users and fewer administrative accounts, which can make management simpler.

However, phishing and malicious QR codes remain possible.

Awareness is still important.

Security Checklist for Dynamic QR Codes

If you create dynamic QR codes, use this checklist.

Choose a reputable QR code provider.

Use HTTPS for destination websites.

Create a strong, unique password.

Enable multi-factor authentication.

Limit administrative access.

Review account activity regularly.

Keep track of active QR codes.

Test QR codes periodically.

Remove outdated or unnecessary codes.

Protect QR codes from physical tampering.

Monitor important destinations for unexpected changes.

Use clear privacy policies when collecting user data.

Avoid collecting personal information unnecessarily.

Train employees to recognize QR-related phishing attempts.

For payment QR codes, verify transaction details.

For users, the checklist is slightly different.

Scan only codes from trusted sources.

Preview the destination URL when possible.

Be suspicious of unexpected QR codes.

Check website addresses carefully.

Do not enter sensitive information on suspicious pages.

Do not install unknown apps because a QR code tells you to.

Verify payment recipients before confirming transactions.

These habits can greatly reduce risk.

Conclusion

Dynamic QR codes are not inherently unsafe.

They are a practical technology that can make digital information easier to access and manage.

Their biggest advantage is flexibility. A business can change the destination behind a printed QR code without printing everything again.

However, that same flexibility creates a security responsibility.

Because the destination can be changed, the system controlling the QR code must be protected. If an attacker gains access to the management account or redirect infrastructure, they may be able to send users somewhere they were never supposed to go.

There is also a separate risk from malicious QR codes created by attackers. A QR code can be used to direct people to phishing websites, fraudulent payment pages, or malicious downloads.
How are ethical hacking services different from penetration testing?How are ethical hacking services different from penetration testing?

Cybersecurity has become a top priority for organizations of every size. As cybercriminals continue to develop more advanced attack techniques, businesses must take proactive measures to protect their systems, networks, and sensitive information.

One of the most effective ways to identify and fix security weaknesses is through penetration testing services. At the same time, many organizations also invest in ethical hacking to strengthen their overall security posture.

Although these terms are often used interchangeably, ethical hacking and penetration testing are not the same. They share similar goals but differ in scope, objectives, methodologies, and outcomes. Understanding these differences helps organizations choose the right approach for their security needs.

This guide explains how ethical hacking services differ from penetration testing, their benefits, and when businesses should use each approach.

Ethical Hacking

Ethical hacking is the authorized practice of attempting to identify vulnerabilities in computer systems, applications, and networks before malicious hackers can exploit them. Ethical hackers work with permission from an organization to uncover weaknesses and recommend improvements.

Unlike cybercriminals, ethical hackers operate within legal boundaries and follow strict rules of engagement. Their goal is to improve security rather than cause damage.

Ethical hacking often involves examining every aspect of an organization's digital infrastructure, including operating systems, cloud environments, wireless networks, mobile applications, APIs, and employee awareness.

What Is Penetration Testing?

Penetration testing is a controlled cybersecurity assessment designed to simulate a real-world cyberattack. The objective is to determine whether vulnerabilities can actually be exploited and what impact a successful attack could have.

Professional penetration testing services focus on specific systems, applications, or networks. Security experts use both automated tools and manual techniques to discover vulnerabilities and safely exploit them under controlled conditions.

The final result is a detailed report showing security weaknesses, exploitation methods, business risks, and remediation recommendations.

Why Businesses Need Security Assessments

Modern organizations face threats such as ransomware, phishing, insider attacks, supply chain compromises, and cloud misconfigurations.

Security assessments help organizations:

  • Discover hidden vulnerabilities.
  • Prevent costly data breaches.
  • Meet regulatory compliance.
  • Protect customer trust.
  • Improve incident response.
  • Reduce financial risk.

Both ethical hacking and penetration testing services contribute to stronger cybersecurity, but they accomplish different objectives.

The Main Difference Between Ethical Hacking and Penetration Testing

The biggest difference lies in their scope.

Ethical hacking is a broad security evaluation that may examine an organization's overall cybersecurity posture. It can involve multiple attack techniques, continuous assessments, policy reviews, and long-term security improvements.

Penetration testing is much narrower. It focuses on testing whether identified vulnerabilities can actually be exploited in a controlled attack scenario.

Think of ethical hacking as a complete security examination, while penetration testing acts as a targeted security test.

Scope of Ethical Hacking

Ethical hacking usually covers:

  • Internal networks
  • External infrastructure
  • Cloud environments
  • Mobile applications
  • APIs
  • Wireless networks
  • Web applications
  • Social engineering
  • Physical security
  • Employee awareness
  • Password security
  • Security policies

Ethical hackers often work over extended periods and may repeatedly assess security as new threats emerge.

Scope of Penetration Testing

Professional penetration testing services generally focus on predefined targets.

Examples include:

  • Company websites
  • Customer portals
  • Internal corporate networks
  • Cloud servers
  • APIs
  • Mobile applications
  • Remote access systems
  • Email security
  • Firewalls

The assessment has clearly defined objectives and timelines.

Objectives of Ethical Hacking

Ethical hacking aims to improve an organization's overall cybersecurity maturity.

Its objectives include:

  • Identifying vulnerabilities
  • Evaluating security controls
  • Improving security awareness
  • Strengthening defenses
  • Discovering hidden attack paths
  • Reducing future cyber risks

Ethical hackers often provide strategic recommendations that help businesses improve long-term security.

Objectives of Penetration Testing

The objective of penetration testing services is much more focused.

The assessment determines:

  • Whether vulnerabilities are exploitable
  • How attackers could gain access
  • What data could be compromised
  • How far attackers could move within the environment
  • The overall business impact

Organizations receive practical evidence showing how an attack could unfold.

Methodology Differences

Ethical hacking often includes:

  • Reconnaissance
  • Vulnerability assessment
  • Security reviews
  • Risk analysis
  • Manual testing
  • Security recommendations
  • Continuous improvement

Meanwhile, penetration testing services generally follow a structured methodology:

Planning

The organization defines testing objectives, scope, timelines, and authorization.

Information Gathering

Testers collect information about the target.

Vulnerability Identification

Security tools identify weaknesses.

Exploitation

Approved vulnerabilities are safely exploited.

Privilege Escalation

Testers determine whether additional access can be obtained.

Post-Exploitation

The impact of successful attacks is evaluated.

Reporting

A detailed report explains findings and remediation steps.

Types of Ethical Hacking

Ethical hacking may involve several specialized areas.

Network Hacking

Testing routers, switches, firewalls, VPNs, and internal networks.

Web Application Hacking

Assessing websites for vulnerabilities such as SQL injection and cross-site scripting.

Cloud Security Testing

Reviewing cloud configurations and permissions.

Wireless Security

Testing Wi-Fi security controls.

Mobile Application Testing

Assessing Android and iOS applications.

Social Engineering

Evaluating employee awareness against phishing and impersonation attacks.

Types of Penetration Testing

Organizations often purchase specialized penetration testing services depending on their environment.

External Penetration Testing

Focuses on internet-facing systems.

Internal Penetration Testing

Assumes an attacker already has internal access.

Web Application Testing

Tests web applications for exploitable vulnerabilities.

API Testing

Evaluates API security.

Wireless Testing

Examines wireless infrastructure.

Cloud Penetration Testing

Focuses on cloud platforms and services.

Mobile Penetration Testing

Evaluates mobile applications for security flaws.

Skills Required

Ethical hackers typically possess broad cybersecurity expertise.

Common skills include:

  • Networking
  • Programming
  • Operating systems
  • Cloud computing
  • Malware analysis
  • Digital forensics
  • Security architecture
  • Threat intelligence

Professionals delivering penetration testing services often specialize in exploit development, vulnerability validation, attack simulation, and reporting.

Common Tools Used

Ethical hackers and penetration testers use many of the same tools.

Popular examples include:

  • Nmap
  • Burp Suite
  • Metasploit
  • Wireshark
  • Nessus
  • OpenVAS
  • Nikto
  • Hydra
  • John the Ripper
  • SQLMap

The difference lies in how these tools are applied during assessments.

Reporting Differences

Ethical hacking reports often include:

  • Overall security posture
  • Risk assessments
  • Security recommendations
  • Policy improvements
  • Employee awareness findings
  • Long-term security roadmap

Reports from penetration testing services usually focus on:

  • Vulnerabilities discovered
  • Exploitation evidence
  • Attack paths
  • Risk ratings
  • Screenshots
  • Technical details
  • Remediation guidance

Compliance Requirements

Many industries require regular security assessments.

Common compliance frameworks include:

  • PCI DSS
  • HIPAA
  • ISO 27001
  • SOC 2
  • GDPR
  • NIST Cybersecurity Framework

Many regulations specifically recommend or require penetration testing services to validate security controls.

Benefits of Ethical Hacking

Organizations gain several advantages:

  • Better visibility into security risks
  • Continuous security improvements
  • Stronger employee awareness
  • Improved incident readiness
  • Reduced attack surface
  • Enhanced cybersecurity maturity

Ethical hacking provides a comprehensive understanding of organizational security.

Benefits of Penetration Testing

Professional penetration testing services offer measurable business value.

Benefits include:

  • Validating security controls
  • Identifying exploitable weaknesses
  • Prioritizing remediation
  • Meeting compliance requirements
  • Reducing breach risks
  • Protecting sensitive information
  • Improving customer confidence

Which Service Should You Choose?

The answer depends on your goals.

Choose ethical hacking when you want:

  • A broad security assessment
  • Continuous testing
  • Long-term cybersecurity improvements
  • Security strategy recommendations

Choose penetration testing services when you need:

  • Compliance validation
  • Exploitation testing
  • Risk verification
  • Security control validation
  • Detailed technical reports

Many organizations benefit from using both approaches together.

Can Ethical Hacking and Penetration Testing Work Together?

Absolutely.

Ethical hacking provides continuous visibility into security risks, while penetration testing services verify whether those risks can actually be exploited.

Together, they create a stronger cybersecurity strategy by combining proactive assessments with realistic attack simulations.

Organizations that use both approaches often detect vulnerabilities earlier, prioritize remediation more effectively, and improve their overall resilience against cyber threats.

Common Misconceptions

Several misconceptions surround these services.

They Are Exactly the Same

Although they overlap, ethical hacking is broader than penetration testing.

Automated Scanners Are Enough

Automated tools identify many vulnerabilities, but they cannot replace human expertise.

Only Large Businesses Need Them

Small and medium-sized businesses are also frequent targets of cyberattacks.

Security Is a One-Time Project

Cybersecurity requires continuous monitoring and regular assessments because threats constantly evolve.

Best Practices for Organizations

To maximize the value of ethical hacking and penetration testing services, organizations should:

  • Conduct regular security assessments.
  • Test internet-facing systems frequently.
  • Include cloud infrastructure in assessments.
  • Train employees on cybersecurity awareness.
  • Patch vulnerabilities promptly.
  • Review user permissions regularly.
  • Monitor security logs continuously.
  • Develop an incident response plan.
  • Perform security assessments after major infrastructure changes.
  • Work with experienced cybersecurity professionals.

Future of Ethical Hacking and Penetration Testing

Emerging technologies continue to reshape cybersecurity.

Artificial intelligence, cloud computing, IoT devices, remote work, and increasingly sophisticated cyber threats require organizations to adopt more advanced security testing methods.

Ethical hackers are expanding their focus to include AI systems, cloud-native applications, containerized environments, and zero-trust architectures. Likewise, penetration testing services are evolving to simulate modern attack techniques that target hybrid infrastructures and interconnected systems.

Organizations that embrace regular security assessments will be better prepared to defend against emerging threats while maintaining customer trust and regulatory compliance.

Conclusion

Ethical hacking and penetration testing play complementary roles in modern cybersecurity, but they are not identical. Ethical hacking provides a broad evaluation of an organization's security posture, identifying weaknesses across people, processes, and technology. Penetration testing, on the other hand, is a focused assessment that safely simulates real-world attacks to determine whether vulnerabilities can be exploited and what impact they could have on the business.

Understanding these differences helps organizations choose the right approach based on their goals, whether improving overall cybersecurity maturity, meeting compliance requirements, or validating the effectiveness of existing security controls. In many cases, combining ethical hacking with penetration testing services offers the strongest defense, providing both strategic insight and practical evidence of security risks.

As cyber threats continue to evolve, investing in regular security assessments is no longer optional. Businesses that proactively identify and address vulnerabilities are better equipped to protect sensitive data, maintain customer confidence, meet regulatory expectations, and build a resilient security posture for the future.

أفضل عيادة خلايا جذعية في تايلاند لعلاج متقدم وتجديد صحيأفضل عيادة خلايا جذعية في تايلاند لعلاج متقدم وتجديد صحي

ما هي خلايا الجذعية ولماذا تعتبر مهمة في الطب التجديدي؟

تُعرف خلايا الجذعية بأنها نوع فريد من الخلايا يمكنها التطور إلى أنواع متعددة من الخلايا المتخصصة في الجسم، مما يجعلها حجر الأساس للطب التجديدي. تتيح هذه الخلايا علاج أمراض مزمنة وإصابات كانت في السابق يصعب شفاؤها، مثل تلف الأنسجة العصبية، أمراض القلب، والتهاب المفاصل. من الناحية العلمية، تشير دراسات متعددة إلى أن العلاجات القائمة على الخلايا الجذعية تزيد من معدلات الشفاء وتقلل الالتهابات، مما يعزز من جودة الحياة.

لماذا تختار تايلاند كوجهة للعلاج بالخلايا الجذعية؟

تتمتع تايلاند بسمعة عالمية في مجال الطب التجديدي، حيث تجمع بين تقنيات طبية متقدمة وكوادر طبية مؤهلة دولياً. تمتاز العيادات التايلاندية باستخدام أحدث الأجهزة والتقنيات المبتكرة التي تدمج بين الخلايا الجذعية والعلاجات الطبيعية لتعظيم الفوائد العلاجية وتقليل المخاطر. بالإضافة إلى ذلك، توفر تايلاند بيئة علاجية متكاملة تشمل خدمات الرعاية الصحية والسياحة العلاجية بأسعار تنافسية مقارنة بالدول الغربية.

معايير اختيار أفضل عيادة خلايا جذعية في تايلاند

عند البحث عن أفضل عيادة خلايا جذعية في تايلاند، يجب التركيز على عدة معايير أساسية تضمن تحقيق النتائج المرجوة بأمان وفعالية:

  • الاعتماد والترخيص الطبي: يجب أن تكون العيادة مرخصة من وزارة الصحة التايلاندية وملتزمة بالمعايير الدولية.
  • فريق طبي متخصص: وجود أطباء وباحثين متخصصين في علم الخلايا الجذعية والطب التجديدي.
  • التقنيات المستخدمة: استخدام تقنيات متقدمة في استخراج، معالجة، وزراعة الخلايا الجذعية.
  • نتائج موثقة: سجلات علاجية واضحة ونتائج إيجابية تم توثيقها سريرياً.
  • دعم المرضى: تقديم خدمات دعم ومتابعة شخصية طوال فترة العلاج وبعده.

تجارب المرضى وأهمية تقييم الجودة

تشير العديد من تجارب المرضى إلى أن أفضل عيادة خلايا جذعية في تايلاند تضمن تقديم علاج مخصص لكل حالة على حدة، حيث يتم تقييم الحالة الصحية بدقة قبل بدء العلاج. هذا النهج الفردي يزيد من فرص النجاح ويقلل من المضاعفات المحتملة. كما أن التقارير الطبية تؤكد أن العيادات الرائدة تستخدم خلايا جذعية مأخوذة من مصادر مختلفة مثل نخاع العظم والدهون، مما يمنح المرضى خيارات متعددة تلائم احتياجاتهم الصحية.

التكنولوجيا والتطور المستقبلي في العيادات التايلاندية

تُعد تايلاند من الدول الرائدة في تطبيق تقنيات الذكاء الاصطناعي وتحليل البيانات الضخمة لتعزيز فعالية العلاجات بالخلايا الجذعية. تستخدم العيادات الحديثة أنظمة متطورة لمراقبة تقدم العلاج وتعديل الجرعات بدقة عالية، ما يعزز من سلامة المريض ويُسرع من عملية التعافي. بالإضافة إلى ذلك، يجري العديد من الأطباء والباحثين في البلاد تجارب سريرية مستمرة لتطوير علاجات جديدة تستهدف أمراضاً متعددة، مما يجعل تايلاند مركزاً حيوياً للابتكار في مجال الطب التجديدي.

نصائح قبل اتخاذ قرار العلاج بالخلايا الجذعية في تايلاند

ينصح الخبراء بضرورة إجراء استشارة طبية متخصصة قبل السفر إلى تايلاند للعلاج بالخلايا الجذعية، بالإضافة إلى التأكد من صحة التشخيص وخطة العلاج. من المهم أيضاً فهم التكاليف المرتبطة بالعلاج والاطلاع على تقييمات المرضى السابقين. يفضل اختيار عيادة توفر شفافية كاملة فيما يتعلق بالمخاطر والفوائد، مع تقديم متابعة مستمرة طويلة الأمد لضمان أفضل النتائج.

خلاصة

تلعب عيادات الخلايا الجذعية في تايلاند دوراً محورياً في تطوير الطب التجديدي، مستفيدة من خبرات طبية عالية وتقنيات متطورة تحسن فرص الشفاء من الأمراض المزمنة والإصابات. اختيار العيادة المناسبة يتطلب معرفة دقيقة بمعايير الجودة والاعتماد الطبي، إلى جانب الاستفادة من تجارب المرضى الحقيقية. في ظل التطورات السريعة في هذا المجال، تبقى تايلاند واحدة من الوجهات الرائدة عالمياً لعلاج الخلايا الجذعية، مما يعزز فرص الصحة والتجدد للجميع.